S119E11 - Security+ - Domain 11 - Governance, Risk, & Compliance
Published: July 6, 2026
Duration: 24:01
Category: Security+ (S119)
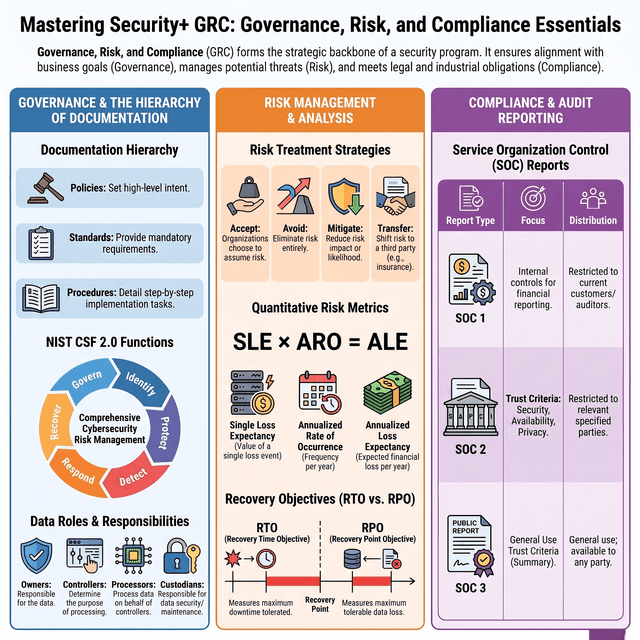
Security+ GRC outlines key knowledge required to assess enterprise security posture. Security governance establishes management’s intent and operational structure through a strict hierarchy of policies (high-level direction), standards (mandatory requirements), and procedures (step-by-step actions).
The risk management lifecycle involves identifying, assessing, and treating risks through avoidance, acceptance, mitigation, or transference. Quantitative risk analysis uses metrics like Single Loss Expectancy (SLE) and Annualized Rate of Occurrence (ARO) to calculate Annualized Loss Expectancy (ALE=SLE×ARO). Even after applying these controls, some residual risk always remains.
Lastly, compliance ensures organizations adhere to...